Too many vulnerabilities. No real priority. KnoxIQ by Appknox is built to prioritize real, exploitable risk and help you fix what matters.

✖
Hamburger_icon_white
VisualEditor_-_Icon_-_Close_-_white

Attackers don't need
your source code.
Neither does Appknox.

Get a free mobile app security scan on the build you actually
ship, before your next release goes out.

No credit card. No source code. No SDK integration. No sales call required.

Group 1597885657

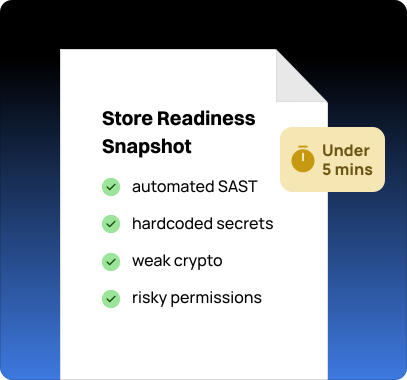
What the free scan report shows

This means you see the shape of your app's risk before anyone asks you for it —
what is weak, what is exposed, and how much of your app you did not write. 

Not the version in your repo. The version on the phone. 

Start with one app. Scale to your portfolio.

The free scan tells you where one build stands today. A paid plan is where the scan stops being an event and becomes part of how you ship.

Every build scanned, triggered from your pipeline
API security testing, from the same run
Findings routed to Jira or Slack
SBOM across every app you ship
Full findings, with remediation guidance
Compliance evidence mapped to your regulator
Agentic DAST on real iOS and Android devices
Store monitoring for apps carrying your brand
Authenticated testing, behind your login
Manual penetration testing — enterprise plans

Compliance evidence means the regulator you answer to — SAMA, RBI, MAS TRM, DORA, PCI-DSS, HIPAA. Appknox does the mapping, so an audit request is a download rather than a project. Store monitoring covers the apps carrying your brand that your team never shipped.

More apps, more often, in more depth.

You still never hand over source code.

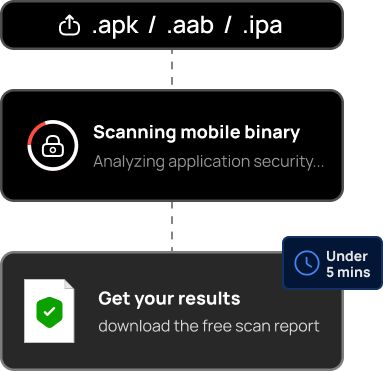
Upload the build you're shipping next 

A compiled APK, AAB, or IPA. No source code, no card, no call. 

In under 5 minutes, you'll have a report on your own binary, covering automated SAST, hardcoded secrets, weak crypto, and risky permissions. 

Know what each one exposes in the app that's already on your users' phones, before anyone exploits it. 

Evaluating across a portfolio? Talk to a security advisor right-arrow-1

Frame 2147223356

Chosen by 500+ security-first teams

Questions about the free mobile app security scan

No. Appknox analyses the compiled binary — the same .apk, .aab, or .ipa your users install. There is no repository to connect, no SDK to integrate, and no build-pipeline change to make.

This means you can scan an app your agency built, a vendor's white-label app, or a legacy build nobody has the source for anymore.